
Infrastructure anchors new IBM agentic security stack
Article excerpt
Highlighted: the sentence this signal was extracted from
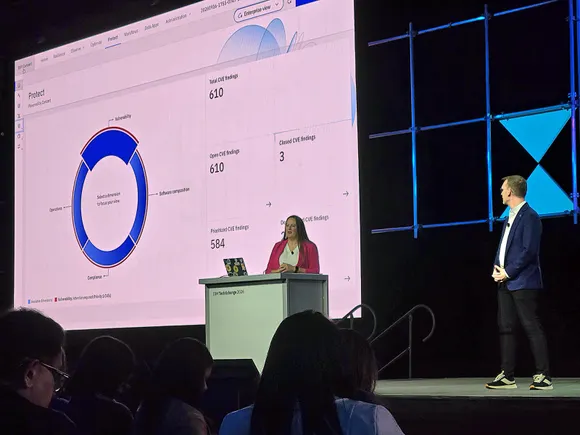
Tools from HashiCorp let IBM's new Agent Identity reach into where agents live and revoke their access to systems, part of a growing trend toward infrastructure-based agent controls. ATLANTA – IBM is the latest enterprise tech vendor to tie agentic security to infrastructure, including an updated version of HashiCorp Vault and Terraform integration with IBM Concert Protect. IBM's agentic AI security updates this week began with the launch of a new Agent Identity product, which contains an agent registry and performs authentication, auditing and compliance for enterprise agents. Agent identity integrates with identity management providers, including IBM Verify, Microsoft Entra, Okta and Ping, along with Vault Enterprise, to issue and revoke short-lived credentials for agents. The combined systems' agentic identity and access management indicates which human operates each agent, limits agent access privileges with 'ceiling' policies, and revokes agent credentials in the case of suspicious activity. HashiCorp Vault Enterprise 2.2, released earlier this month, now supports on-premises application startup authentication using a trusted platform module (TPM). This VM provides cryptographic proof that the application possesses a valid encryption key, which Vault can verify before granting its first access, thereby eliminating the need to reuse 'bootstrap' credentials. VMs can also...
Keep reading with a free account
The rest of this article, and every signal for HashiCorp, is in your free account.